01
Your app asks for access
A registered app starts an OAuth 2.0 authorization-code flow with PKCE. The request asks only for the scopes it needs.
A predictable connection flow for apps that need to use a customer’s existing payment account.
A registered app starts an OAuth 2.0 authorization-code flow with PKCE. The request asks only for the scopes it needs.
The user consents and connects their own Snippe or Abliner account. Provider credentials stay on the server side.
The app uses its scoped token. CamelPay validates the request and routes the supported operation to the connected provider.
Provider responses and signed callbacks help an app follow status. An acceptance response is not proof of final payment or settlement.
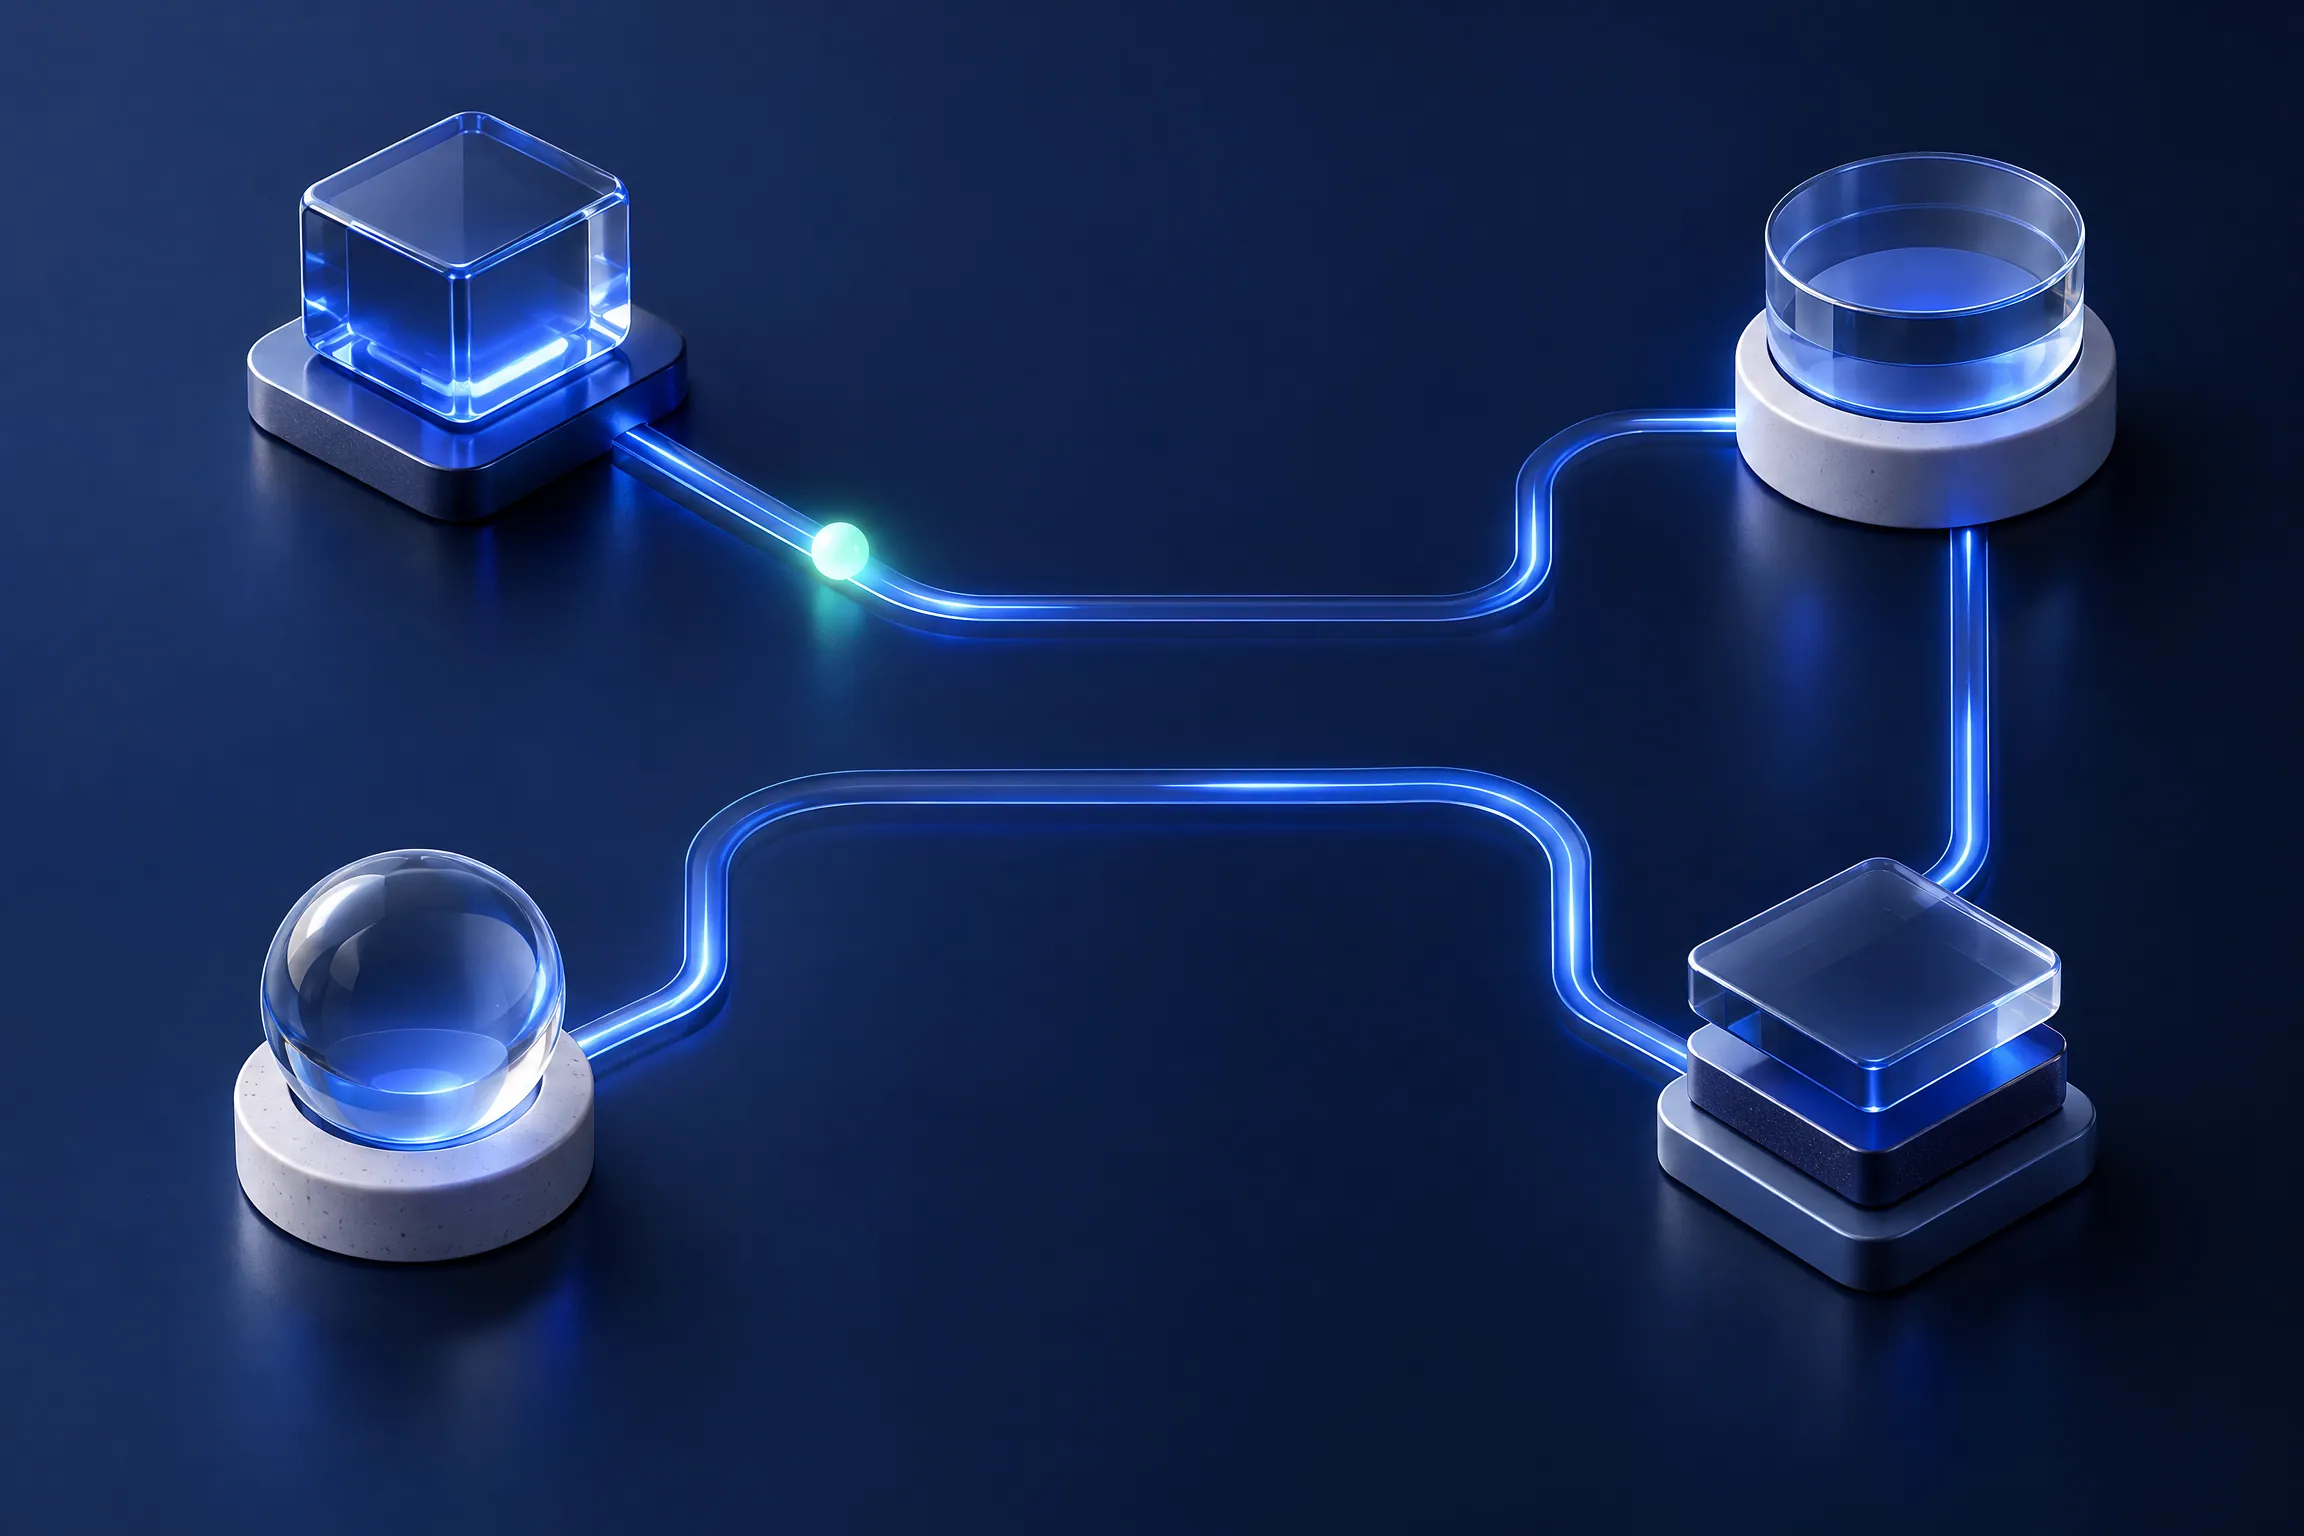
Each hop is explicit. The application requests scoped access. CamelPay verifies the request and passes supported operations through. The provider decides what happens next.
Authorizes, validates, routes, and helps correlate supported provider requests and callbacks.
Controls account eligibility, methods, execution, fees, delivery, reversals, settlement, and final status.
202 Accepted response means the provider accepted the request. It does not guarantee that funds moved or settled. For uncertain outcomes, reconcile with the provider before creating a new operation.Start from the API schema and provider notes rather than assumptions.